
 By
·
5 minute read
Every time a supplier sends an end-of-life notice, we get a version of the same question: "How do you know which products and roadmaps are affected when a shared module changes?"
The truth is, finding every product that uses the module is where the work starts, not where it ends. The list tells you where to look, but it doesn't tell you what needs to change.
For instance, a controller retirement might touch five products but require an immediate decision on only two. Meanwhile, a shared module revision might leave one roadmap intact while disrupting another product's firmware validation, regional certification, or launch timing.
A useful shared module impact analysis traces the change outward until product leaders can answer one question: Which decisions were based on an assumption that is no longer true?
The meaningful impact usually shows up there.
Most manufacturers can already pull a where-used list in minutes. What they lack is a way to see which of those products now face a different launch, certification, or lifecycle decision.
The steps below show how to assess the impact of a shared module change from the first dependency to a decision-ready answer.
Why Where-Used Lists Are Not Enough
Across anonymized field conversations held with Gocious, teams often know that a component, module, requirement, or date changed. The harder work is reconstructing what else that change affects across products, timing, software, regions, and business commitments.
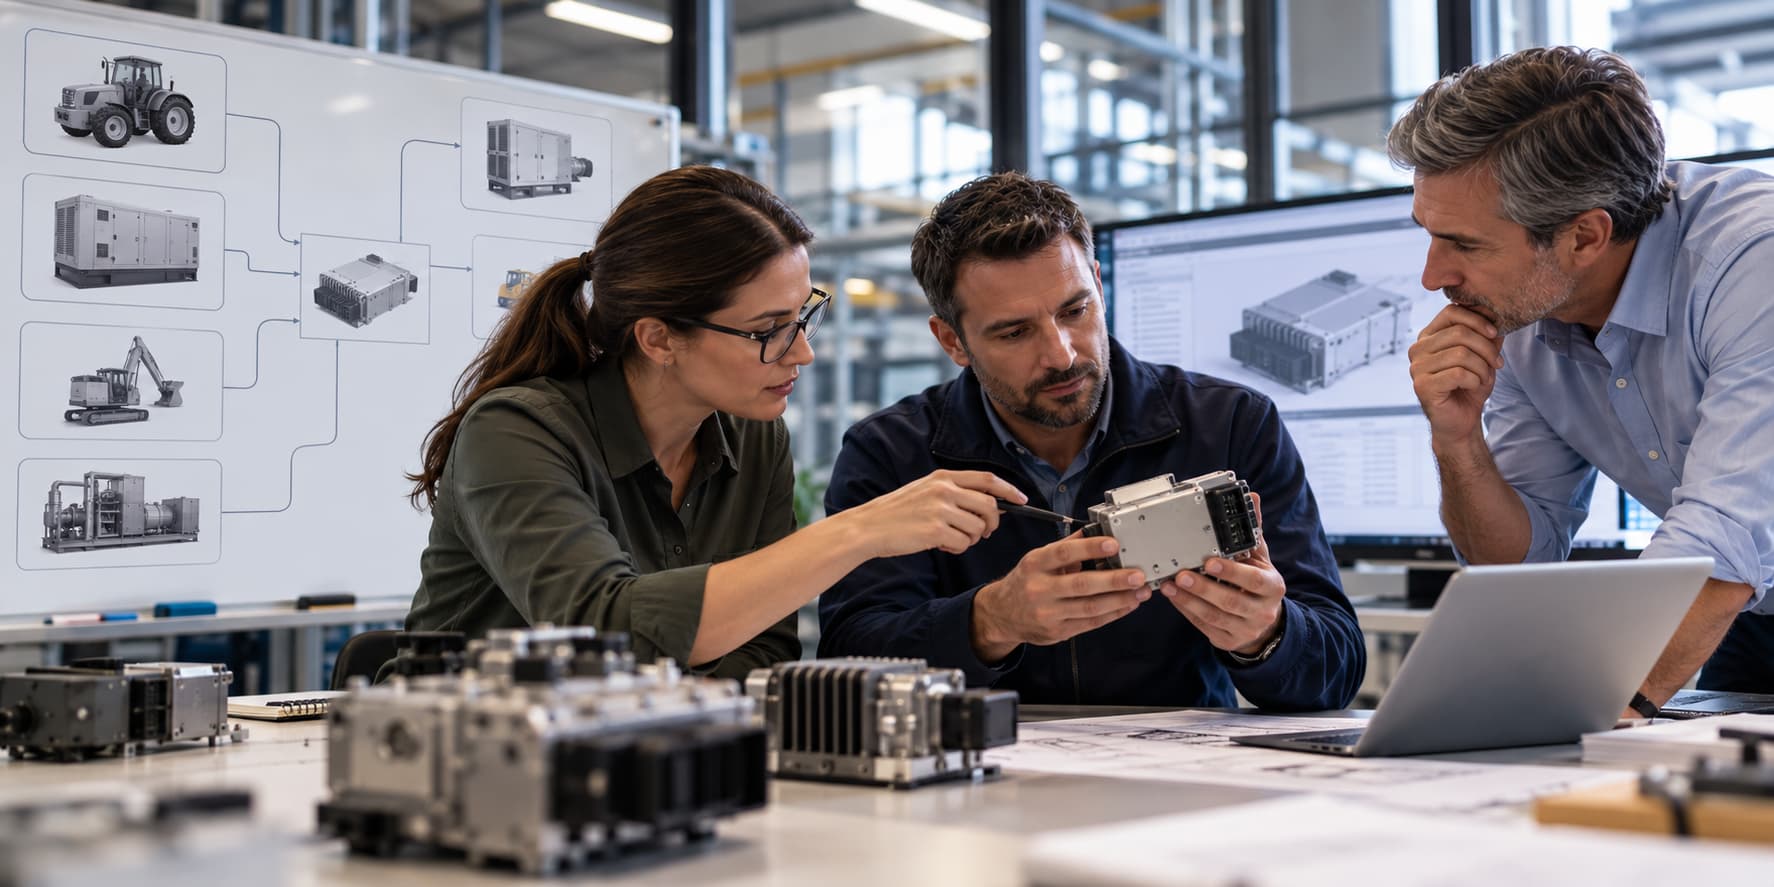
Engineering research has studied this for years. Work on design change propagation across modules shows that even in modular products designed to be loosely coupled, a change in one module can still travel through its interfaces into others.
At the portfolio level, the same propagation runs through product dependencies and plans rather than physical interfaces.
How Do You Trace the Impact of a Shared Module Change?
One of the first actions we recommend you take is to start with one change. Let’s look at a quick example.
Suppose an equipment manufacturer uses the same controller across several product lines. The supplier announces that the current controller will reach end of life in 18 months, and a replacement is available, but it requires different firmware and another validation cycle.
The current controller supports five products:
- Product A: Mature product expected to remain active for four more years
- Product B: Major refresh launching next year
- Product C: European configuration requiring separate certification
- Product D: Product retiring in nine months
- Product E: Next-generation platform still in development
At the component level, all five products are affected. At the planning level, they're affected very differently.
What Is the First-Order Impact?
First, identify the direct dependencies. Find every important active product, future product, product generation, regional variant, and platform that currently uses or plans to use the module.
|
Product |
Current relationship |
Initial exposure |
|
Product A |
Uses current controller |
Supply continuity |
|
Product B |
Current controller planned for launch |
Launch and validation |
|
Product C |
Controller used in EU configuration |
Certification |
|
Product D |
Uses current controller |
Limited because retirement is near |
|
Product E |
Architecture not yet frozen |
May adopt replacement directly |
The answer shouldn't be "Five products have a controller problem." Here’s why.
Product D may require little more than confirming inventory through retirement. Product E may be early enough to adopt the replacement without disturbing a committed launch, and Product B may have the most urgent exposure.
This is why shared module risk needs product and lifecycle context, not simply a list of everywhere the component appears. Visualizing product dependencies makes this context far easier to read.
What Is the Second-Order Impact?
Now ask what else was built around the old assumption.
The replacement controller requires different firmware. The firmware change affects Product B's validation schedule, validation supports its planned launch, and the launch is tied to an important customer commitment.
The impact chain looks like this:
Controller retirement → Replacement controller → Firmware change → Additional validation → Launch timing → Customer commitment
The customer doesn't depend directly on the controller, but the roadmap commitment does. A component search alone can miss this second-order impact, much like the way supply chain delays affect software launch timing through validation rather than directly.
For every important relationship, ask what decision, assumption, or promise depended on it remaining unchanged.
Can the Same Module Change Affect Different Products Differently?
Yes. Product C creates a different impact chain:
Controller revision → Hardware configuration changes → Existing certification evidence may no longer apply → Regional validation or approval is required → European transition timing changes
Product B needs a launch conversation. Product C needs a certification and regional timing conversation, and Product D may need only a supply decision. Same module change, different product consequence. Regulated regions in particular need compliance planning built into the roadmap.
How Do You Separate "Connected" From "Needs Action"?
Not every dependency deserves an escalation. A useful classification looks like this:
|
Impact state |
Meaning |
|
No material impact |
The product uses the module, but no meaningful roadmap, lifecycle, or customer commitment changes |
|
Monitor |
The product could be affected, but no immediate decision is required |
|
Plan adjustment |
A roadmap, regional plan, lifecycle assumption, or release needs to move |
|
Leadership decision |
The change creates a meaningful tradeoff involving timing, investment, scope, customers, or another portfolio priority |
This keeps one shared-module change from creating ten unnecessary executive discussions.
How the Classification Applies to Each Product
Product D might have no material impact if existing inventory covers its remaining product life. Product A might sit at "monitor" if there's time to plan its transition. Product C may require a plan adjustment because certification timing changes, and Product B may require a leadership decision if the module transition threatens a committed launch.
Why Does Lifecycle Timing Change the Impact?
The same dependency has different importance at different points in a product's life. For instance, let’s suppose the controller reaches the end of supply in December 2028.
|
Product |
Lifecycle position |
Likely response |
|
A |
Active through 2031 |
Transition required |
|
B |
Launches in 2028 |
Resolve before launch |
|
C |
Regional support through 2032 |
Certification and transition decision |
|
D |
Retires in early 2028 |
Potential last-time buy |
|
E |
Future generation |
Adopt replacement before architecture freezes |
A static dependency diagram says "five affected products." Meanwhile, a lifecycle-aware view says two immediate decisions, one regional transition, one supply action, and one future architecture update, which is far more useful for leadership.
Pro-Tip: When the change is a full retirement rather than a revision, How to Track Module Retirement Across Regional Product Lines walks through the transition planning in detail.
What Should Shared Module Impact Analysis Produce?
Shared module impact analysis should end with something decision-ready. For every materially affected product, capture six answers:
- What changed? The shared controller reaches end of life.
- Which assumption is no longer valid? The current controller remains available through the planned product life.
- What commitment is affected? Launch timing, software capability, regional approval, support period, or lifecycle transition.
- When is a decision required? Before validation begins, before a last-time buy, or before platform architecture freezes.
- What is the proposed response? Transition, redesign, purchase inventory, resequence, or continue unchanged.
- Who owns the decision? The product, platform, or portfolio leader accountable for the commitment.
Leadership can then move from "This controller appears in five products" to "Product B's launch, Product C's certification, and Product A's lifecycle transition need decisions. Product D does not." This is what impact analysis is for, and it's the focus of our product dependency change impact capabilities.
How Do You Avoid Rebuilding the Dependency Story After Every Change?
Connect the important relationships before the disruption occurs.
Detailed engineering and PLM systems should continue controlling technical product structure and change management, which academic work on engineering change management treats as its own discipline.
The strategic planning layer needs something different. It needs enough connection among products, major modules, roadmaps, regions, lifecycle timing, and commitments to understand the product consequence when one relationship changes, which is the heart of managing lifecycle and dependency risk.
Trace Module Changes to Decisions With Gocious
Gocious is a product portfolio visibility platform that helps complex manufacturers maintain this planning context without replacing detailed engineering systems. Our software helps product and portfolio teams move from identifying where a shared component exists to understanding which roadmap, lifecycle, regional, or portfolio decisions may now require attention, as part of broader product portfolio planning.
Ready to see which decisions a module change really touches?
Explore Gocious Product Portfolio Planning or request your custom demo.